Getting started with Neon Data API
This guide walks you through enabling the Data API, creating a table with RLS, and running your first query. The Data API has no permission layer of its own. Every request is authorized entirely by yo...
This guide walks you through enabling the Data API, creating a table with RLS, and running your first query.
Before you begin
Section titled “Before you begin”- The Neon Data API is enabled at the branch level for a single database. Each branch has its own Data API configuration, so you must select the correct branch before enabling the API.
- Neon Data API does not currently support projects with IP Allow or Private Networking enabled.
Enable the Data API
\1. Navigate to the Data API page
In the Neon Console, select your project and select Postgres database > Data API.
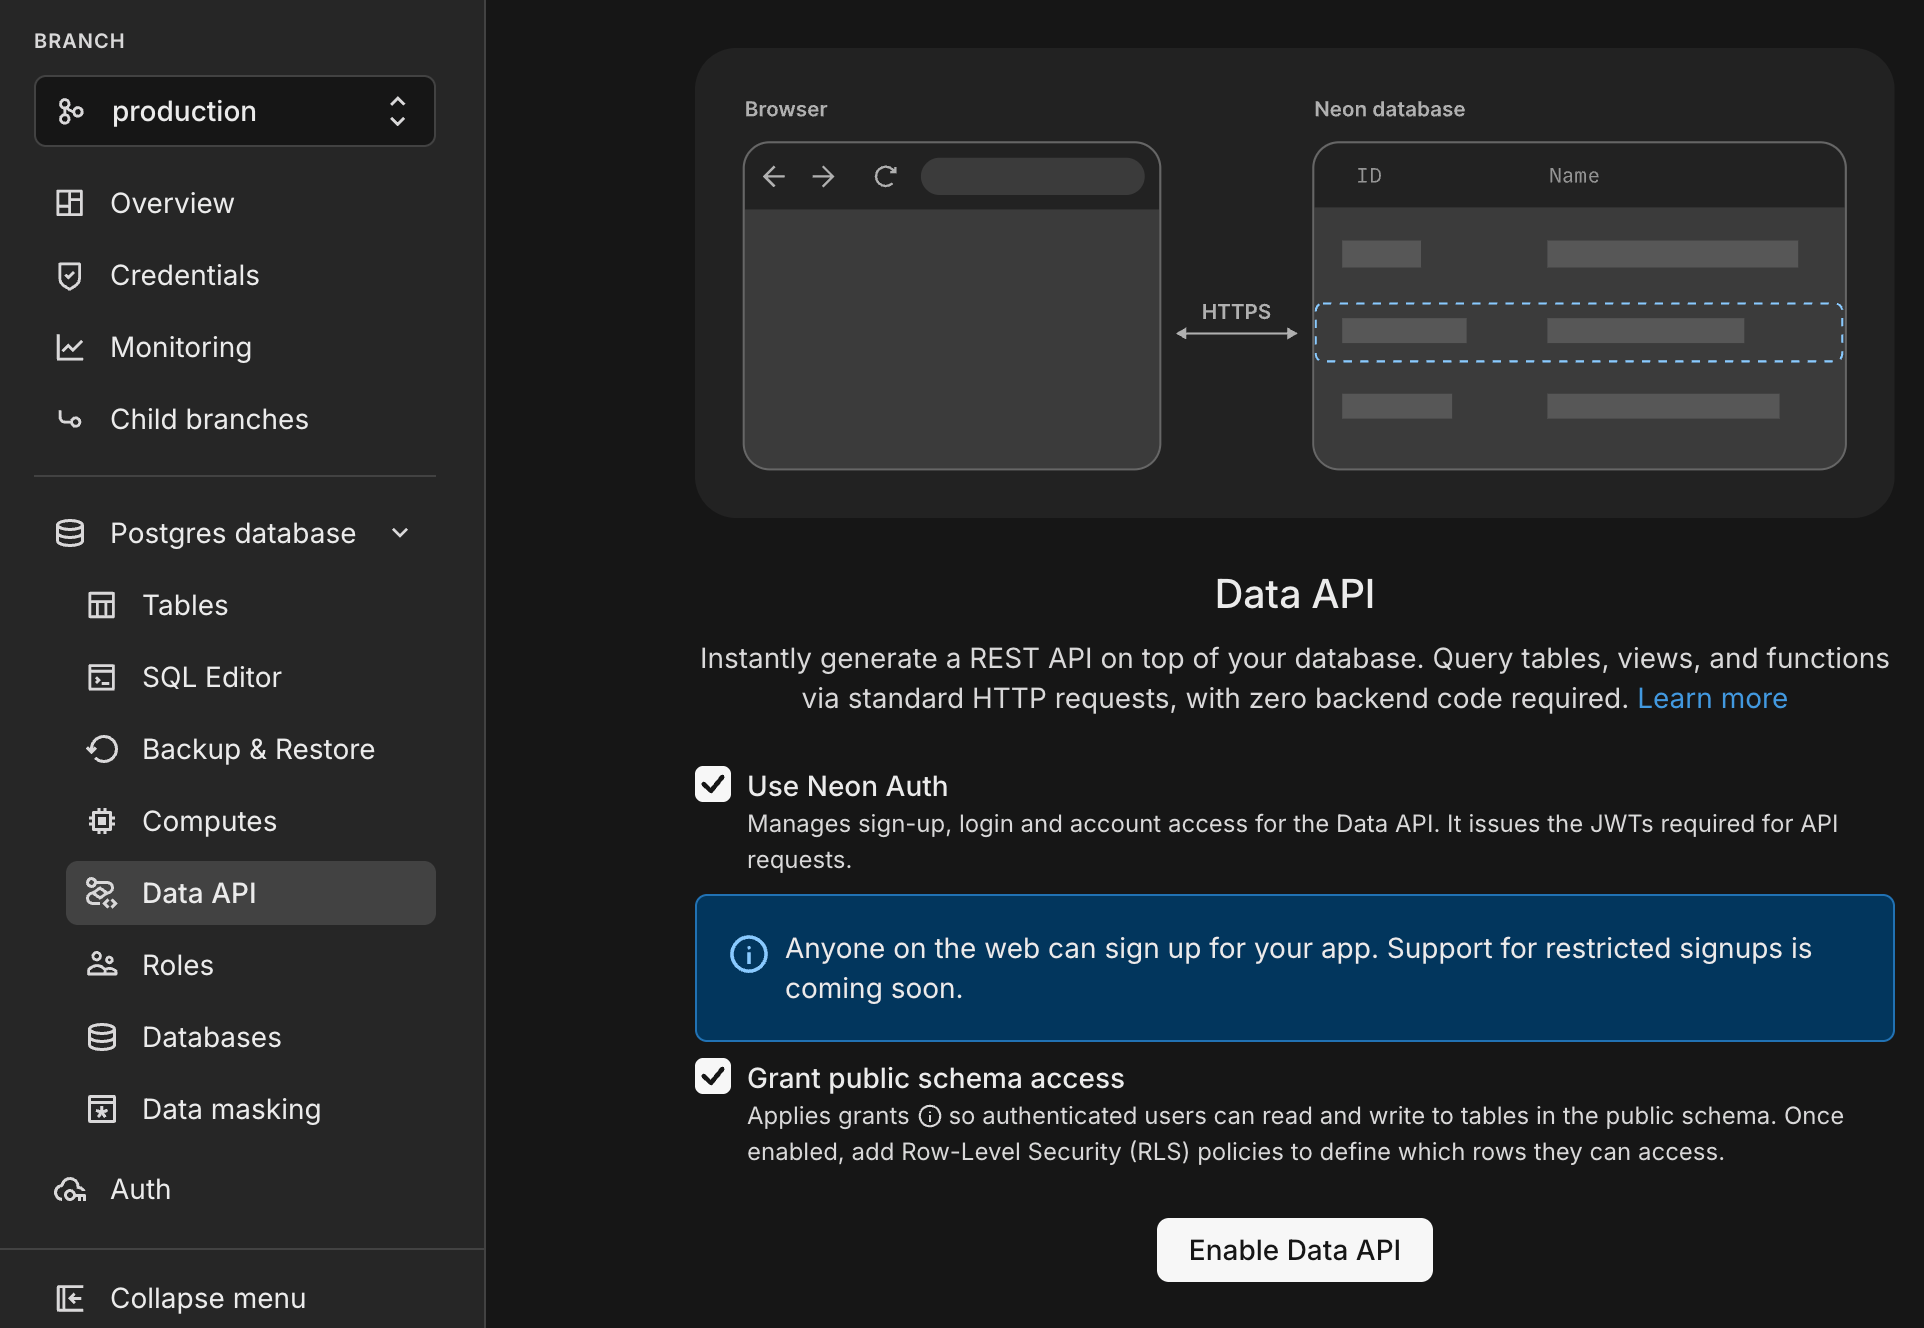
\2. Configure authentication
The Data API uses JWTs for access control. Configure a provider now or later from the Settings tab. For public data that doesn't require login, use the
anonymousrole instead.- Managed Better Auth: Check the Use Managed Better Auth checkbox to enable Managed Better Auth as your provider. Managed Better Auth manages sign-up, login, and account access, issuing the JWTs required for API requests.
- Other providers: Leave the checkbox unchecked and configure your provider (such as Auth0, Clerk, or Firebase Auth) later. See Custom authentication providers for setup instructions.
\3. Configure schema access (optional)
The Grant public schema access checkbox automatically applies database permissions so the
authenticatedrole can read and write to tables in thepublicschema.View the GRANT statements applied
SQL -- Schema usage GRANT USAGE ON SCHEMA public TO authenticated; -- For existing tables GRANT SELECT, UPDATE, INSERT, DELETE ON ALL TABLES IN SCHEMA public TO authenticated; -- For future tables ALTER DEFAULT PRIVILEGES IN SCHEMA public GRANT SELECT, UPDATE, INSERT, DELETE ON TABLES TO authenticated; -- For sequences (for identity columns) GRANT USAGE, SELECT ON ALL SEQUENCES IN SCHEMA public TO authenticated;Enable this checkbox unless you need to manage permissions manually. If you leave it unchecked, see Access control for details on granting permissions yourself.
\4. Enable Data API
Click Enable Data API to activate the Data API. Once enabled, you'll see the Data API page.
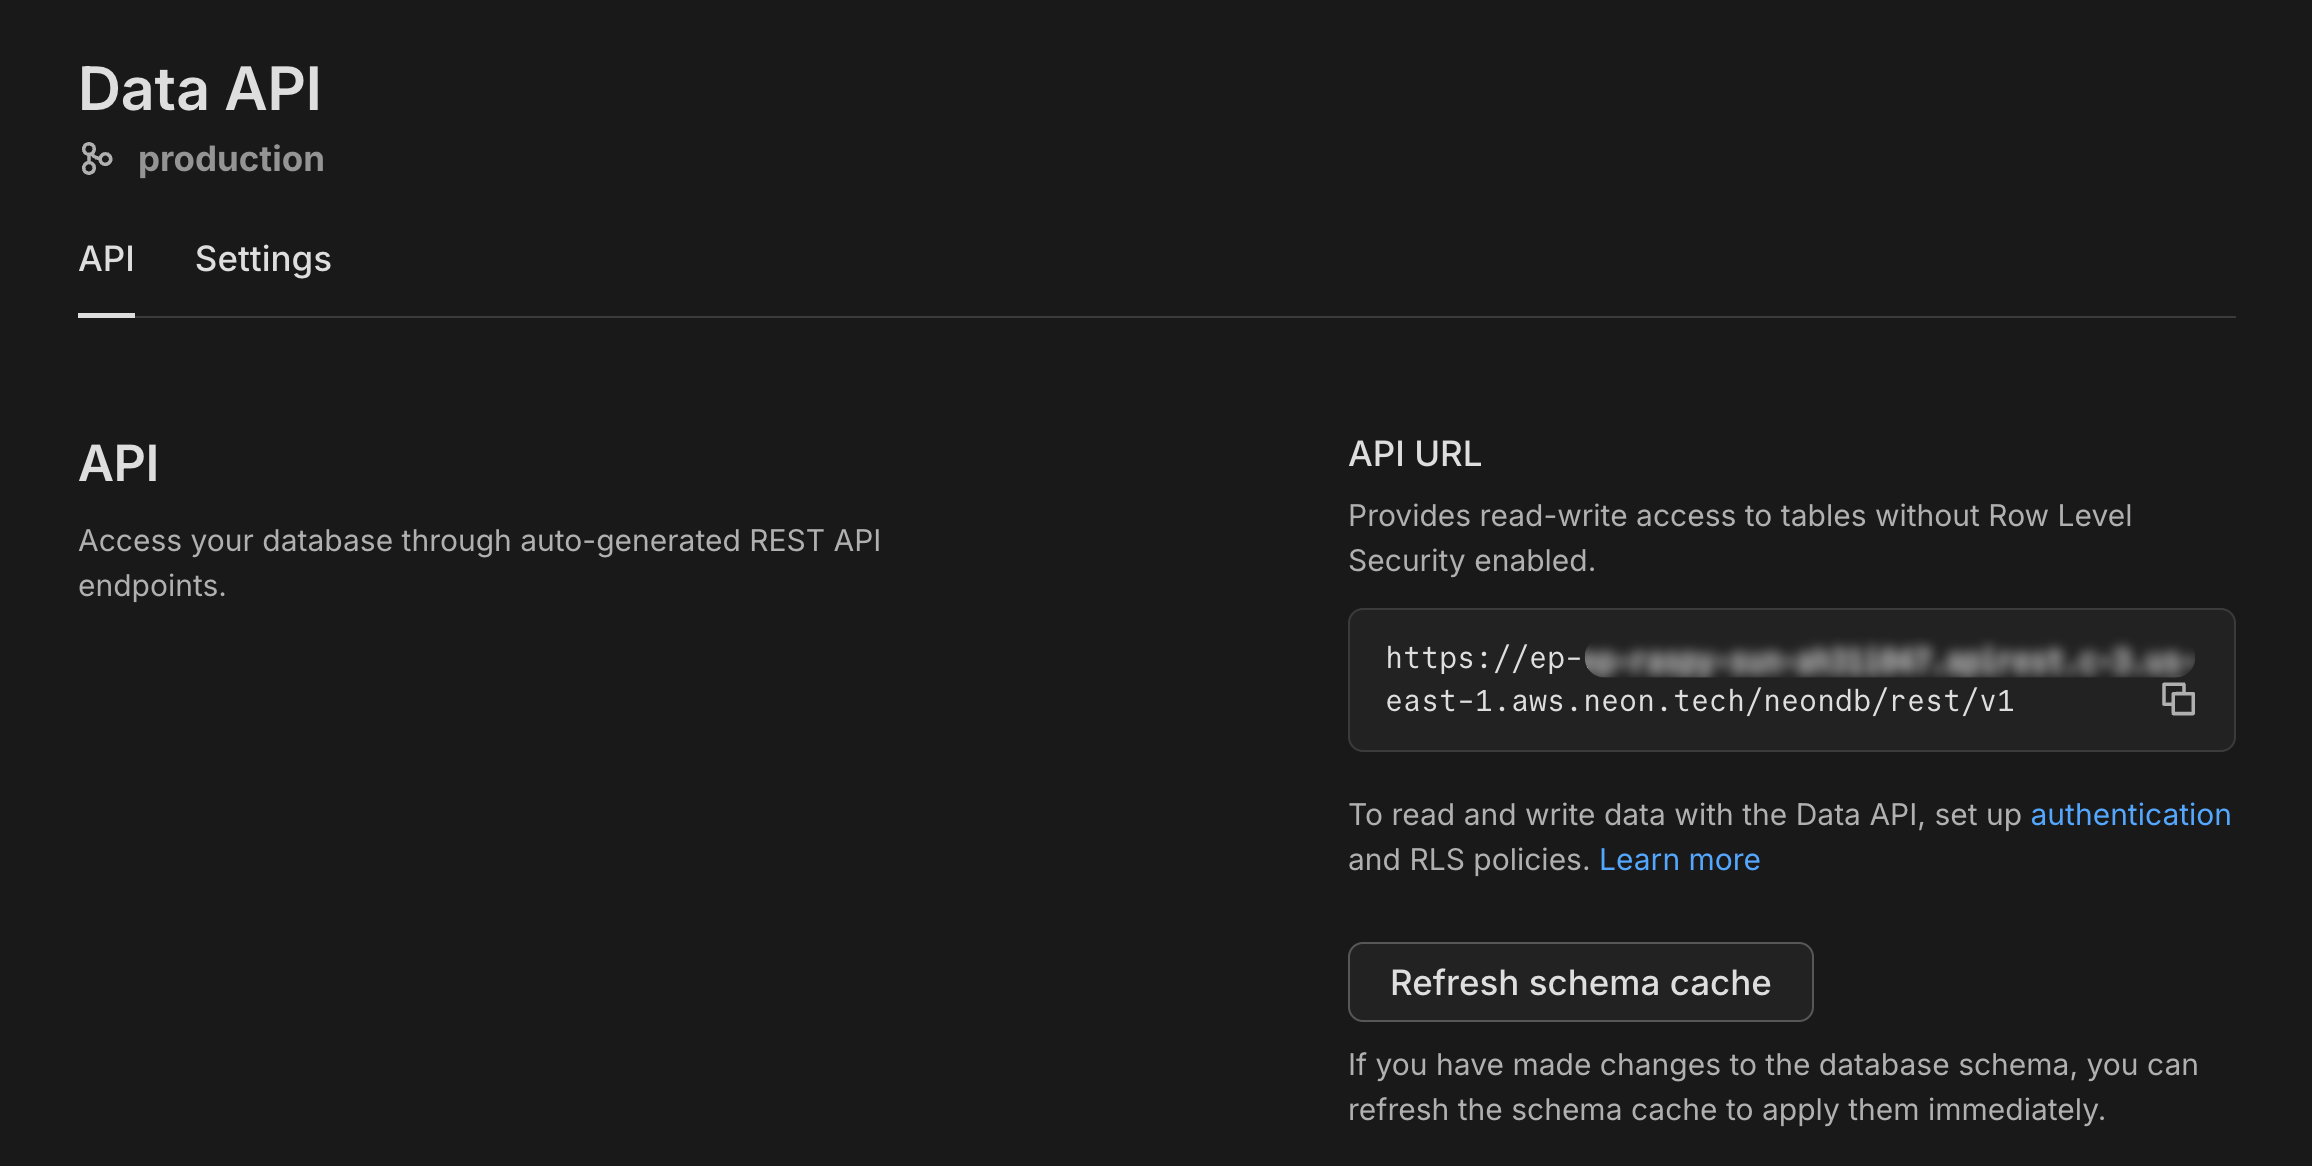
On the API tab, you'll see:
- API URL: Your REST API endpoint for accessing your database
- Refresh schema cache: A button to update the Data API when you make schema changes
- Security section: Options to configure authentication and enable Row-Level Security on your tables
For advanced configuration options like custom authentication providers, exposed schemas, and CORS settings, see the Settings tab or refer to Managing the Data API.
Next, you'll create a table with Row-Level Security (RLS) policies to define which rows users can access.
Create a table with RLS
The Data API interacts directly with your Postgres schema. Because the API is accessible over the internet, it's crucial to enforce security at the database level using PostgreSQL's Row-Level Security (RLS) features.
In this example, we'll create a
poststable where users can read published posts and manage their own posts securely. Choose the approach that matches how you manage your database schema:- SQL: Write SQL directly in the Neon SQL Editor or manage migrations manually. See our PostgreSQL RLS tutorial for more on RLS fundamentals.
- Drizzle (crudPolicy): A high-level helper that generates RLS policies in one declaration. Best for simple cases where read and modify permissions follow the same pattern.
- Drizzle (pgPolicy): Define policies per operation or use a single
FOR ALLpolicy. Use this when you need different logic for different operations (for example, time-limited updates, different rules for INSERT vs UPDATE).
For more on Drizzle RLS, see our Drizzle RLS guide.
SQL -- This script creates a posts table, enables RLS, and defines two policies: -- one allows authenticated users to read published posts, and the other -- gives users full access (read, insert, update, delete) to their own posts. -- 1. Create the table CREATE TABLE posts ( id bigint GENERATED BY DEFAULT AS IDENTITY PRIMARY KEY, user_id text DEFAULT (auth.user_id()) NOT NULL, content text NOT NULL, is_published boolean DEFAULT false, "created_at" timestamp with time zone DEFAULT now() NOT NULL ); -- 2. Enable RLS ALTER TABLE posts ENABLE ROW LEVEL SECURITY; -- 3. Read published posts CREATE POLICY read_published_posts ON posts FOR SELECT TO authenticated USING (is_published = true); -- 4. Full access to own posts CREATE POLICY manage_own_posts ON posts FOR ALL TO authenticated USING (auth.user_id() = user_id) WITH CHECK (auth.user_id() = user_id);TypeScript // This schema defines the same two-policy behavior using Drizzle ORM. The crudPolicy // helper generates equivalent RLS: `read` allows published posts or own posts, // and `modify` restricts insert, update, and delete to own posts. import { sql } from 'drizzle-orm'; import { crudPolicy, authenticatedRole, authUid } from 'drizzle-orm/neon'; import { bigint, boolean, pgTable, text, timestamp } from 'drizzle-orm/pg-core'; export const posts = pgTable( 'posts', { id: bigint({ mode: 'number' }).primaryKey(), userId: text('user_id') .notNull() .default(sql`(auth.user_id())`), content: text().notNull(), isPublished: boolean('is_published').notNull().default(false), createdAt: timestamp('created_at', { withTimezone: true }).notNull().defaultNow(), }, (table) => [ crudPolicy({ role: authenticatedRole, read: sql`is_published OR (auth.user_id() = ${table.userId})`, modify: authUid(table.userId), }), ] );TypeScript // This schema defines the same two-policy behavior using Drizzle ORM with pgPolicy. // One policy allows reading published posts; the other gives full access to own posts. import { sql } from 'drizzle-orm'; import { authenticatedRole, authUid } from 'drizzle-orm/neon'; import { bigint, boolean, pgPolicy, pgTable, text, timestamp } from 'drizzle-orm/pg-core'; export const posts = pgTable( 'posts', { id: bigint({ mode: 'number' }).primaryKey(), userId: text('user_id') .notNull() .default(sql`(auth.user_id())`), content: text().notNull(), isPublished: boolean('is_published').notNull().default(false), createdAt: timestamp('created_at', { withTimezone: true }).notNull().defaultNow(), }, (table) => [ pgPolicy('read_published_posts', { to: authenticatedRole, for: 'select', using: sql`is_published = true`, }), pgPolicy('manage_own_posts', { to: authenticatedRole, for: 'all', using: authUid(table.userId), withCheck: authUid(table.userId), }), ] );Info: What is auth.user_id() and authUid()?
auth.user_id()returns the JWTsubclaim astext. Useauth.uid()instead if youruser_idcolumn isuuid; it parsessubas a UUID and returnsNULLif it's not valid.authUid()is a Drizzle helper forauth.user_id().Refresh schema cache
The Data API caches your database schema for performance. When you modify your schema (adding tables, modifying columns, or changing structure, etc.), you need to refresh this cache for the changes to take effect.
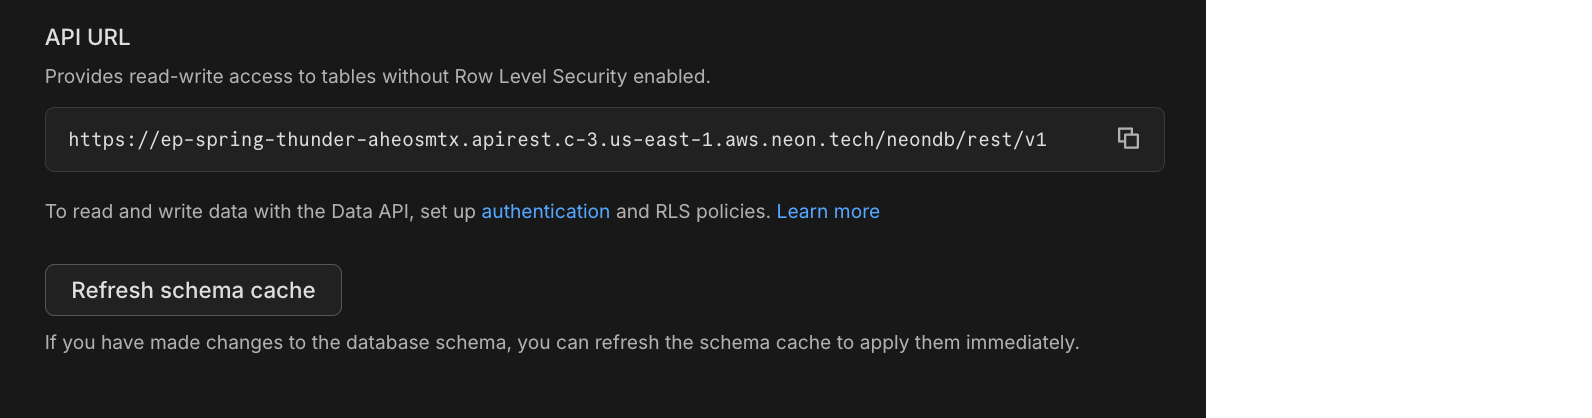
Option 1: Neon Console
Go to Postgres database > Data API in the Neon Console and click Refresh schema cache.
Option 2: Neon API
You can also refresh the schema cache programmatically. The
PATCH /projects/{project_id}/branches/{branch_id}/data-api/{database_name}endpoint always refreshes the schema cache as part of the operation. Send an empty body to trigger a refresh:Bash curl -X PATCH 'https://console.neon.tech/api/v2/projects/{project_id}/branches/{branch_id}/data-api/{database_name}' \ -H 'Authorization: Bearer YOUR_NEON_API_KEY' \ -H 'Content-Type: application/json' \ -d '{}'Connect and Query
You can connect to the Data API using a client library or direct HTTP requests.
Option 1: Using a client library
Install a client library and run your first query. Choose the option that matches your authentication provider:
Use
@neondatabase/neon-jsif you're using Managed Better Auth. This library handles token management automatically.1. Install
Bash npm install @neondatabase/neon-js2. Usage
TypeScript import { createClient } from '@neondatabase/neon-js'; // Initialize with Managed Better Auth // Use your Neon database URL without credentials or query parameters. // Example: https://ep-example.c-2.us-east-1.aws.neon.tech/neondb const client = createClient(import.meta.env.VITE_NEON_DATABASE_URL); // Query - the JWT token is injected automatically when the user is signed in const { data, error } = await client .from('posts') .select('*') .eq('is_published', true) .order('created_at', { ascending: false }); console.log(data);Use
@neondatabase/postgrest-jswith any authentication provider that issues JWTs, such as Auth0, Clerk, or Firebase Auth.1. Install
Bash npm install @neondatabase/postgrest-js2. Usage
Provide a function that retrieves the JWT token from your authentication system. This token is included in each request to enforce RLS policies.
TypeScript import { fetchWithToken, NeonPostgrestClient } from '@neondatabase/postgrest-js'; const getTokenFromAuthSystem = async (): Promise<string> => { // Retrieve the JWT token from your auth system (e.g., Auth0, Clerk, Firebase) return 'your-jwt-token'; }; // Get your URL from the Neon Console or run: neon data-api get const client = new NeonPostgrestClient({ dataApiUrl: import.meta.env.VITE_NEON_DATA_API_URL, options: { global: { fetch: fetchWithToken(getTokenFromAuthSystem), }, }, }); // Query const { data, error } = await client .from('posts') .select('*') .eq('is_published', true) .order('created_at', { ascending: false }); console.log(data);For detailed guidance on performing
INSERT,UPDATE,DELETE, and advanced queries (filters, joins, stored procedures, etc.) in either case, refer to the Neon Javascript SDK documentation.For detailed guidance on performing
INSERT,UPDATE,DELETE, and advanced queries (filters, joins, stored procedures, etc.) in either case, refer to the Neon Javascript SDK documentation.Option 2: Direct HTTP requests
Query the Data API directly using any HTTP client. Include the
Authorizationheader with a valid JWT token from your authentication provider. The token must include asubclaim for RLS policies to work correctly.Where to get the JWT token:
- Your auth provider's SDK: Retrieve the token using your provider's API (for example,
getAccessToken()in Auth0,getToken()in Clerk). - Managed Better Auth: Retrieve the token using
client.auth.getSession()from the@neondatabase/neon-jslibrary (see Get current session), or use the Auth API reference UI for manual testing (see Testing with Managed Better Auth below).
About the
subclaim:For RLS policies to work correctly, the JWT token must include a
sub(subject) claim, which contains the user's unique identifier. The Data API uses this claim to enforce Row-Level Security policies via theauth.user_id()function. Most authentication providers include this claim by default.Example: SELECT (GET)
This request queries the
poststable for all published posts, ordered by most recent first:Bash curl -X GET 'https://your-data-api-endpoint/rest/v1/posts?is_published=eq.true&order=created_at.desc' \ -H 'Authorization: Bearer YOUR_JWT_TOKEN' \ -H 'Content-Type: application/json'Example: INSERT (POST)
This request inserts a new row into the
poststable, setting thecontentcolumn:Bash curl -X POST 'https://your-data-api-endpoint/rest/v1/posts' \ -H 'Authorization: Bearer YOUR_JWT_TOKEN' \ -H 'Content-Type: application/json' \ -d '{"content": "Hello world"}'For UPDATE, DELETE, filtering, and other operations, see the PostgREST documentation.
- Your auth provider's SDK: Retrieve the token using your provider's API (for example,
Testing with Managed Better Auth
Section titled “Testing with Managed Better Auth”If you're using Managed Better Auth and want to test the Data API without building an application first, you can obtain a JWT token using the interactive Auth API reference UI or any HTTP client (the examples below use cURL). If you're using a different provider, obtain JWT tokens through your provider's authentication flow and use them in the Authorization: Bearer header as shown in the HTTP examples above.
The Auth API reference UI is an interactive browser-based tool for exploring and testing all Managed Better Auth endpoints. It is powered by Better Auth's OpenAPI plugin.
- Open the Auth API reference: Navigate to your Auth URL with
/referenceappended, for example,https://ep-example.neonauth.us-east-1.aws.neon.tech/neondb/auth/reference. You can find your Auth URL on the Auth page, Configuration tab in the Neon Console. - Create a test user: Use the UI to call
POST /sign-up/emailwith a JSON body:JSON { "email": "test@example.com", "password": "your-password", "name": "Test User" } - Or sign in with an existing user: Call
POST /sign-in/emailwith:JSON { "email": "test@example.com", "password": "your-password" } - Get the JWT token: Call
GET /get-sessionand copy the JWT from theSet-Auth-Jwtresponse header. - Query the Data API: Use the JWT in your requests:
Bash curl -X GET 'https://your-data-api-endpoint/rest/v1/posts' \ -H 'Authorization: Bearer YOUR_JWT_TOKEN' \ -H 'Content-Type: application/json'
The following steps walk through signing up, obtaining a JWT, and querying the Data API from the terminal. You can find your Auth URL on the Auth page and your Data API URL on the Data API page in the Neon Console.
1. Sign up (or sign in)
Create a test user. The -c flag saves the session cookie returned by Managed Better Auth:
curl -X POST 'https://ep-example-auth.neonauth.us-east-1.aws.neon.tech/neondb/auth/sign-up/email' \
  -c cookies.txt \
  -H 'Content-Type: application/json' \
  -H 'Origin: http://localhost:3000' \
  -d '{"email":"test@example.com","password":"your-password","name":"Test User","callbackURL":"http://localhost:3000"}'
To sign in with an existing user instead, replace /sign-up/email with /sign-in/email and omit the name and callbackURL fields.
2. Get the JWT token
Call get-session using the saved cookie (-b). The -D - flag prints response headers to your terminal. Look for the set-auth-jwt header and copy its value:
curl 'https://ep-example-auth.neonauth.us-east-1.aws.neon.tech/neondb/auth/get-session' \
  -b cookies.txt \
  -H 'Origin: http://localhost:3000' \
  -D - -o /dev/null
The output will include a line like:
set-auth-jwt: eyJhbGci...Copy the full token value.
3. Query the Data API
Use the JWT as a bearer token to query your table:
curl 'https://ep-example.apirest.us-east-1.aws.neon.tech/neondb/rest/v1/posts?select=*' \
  -H 'Authorization: Bearer YOUR_JWT_TOKEN'
Tip: Token expiration
JWTs expire after approximately 15 minutes. If you receive a "JWT token has expired" error, sign in again to get a fresh token.
Query patterns
Section titled “Query patterns”The Data API supports full CRUD operations and advanced queries. Here's a quick reference of the most common methods available in the Neon TypeScript SDK:
CRUD operations
Section titled “CRUD operations”| Operation | Method | Example | SDK Reference |
|---|---|---|---|
| Select | .select() |
client.from('posts').select('*') |
select |
| Insert | .insert() |
client.from('posts').insert({ title: 'New post' }) |
insert |
| Update | .update() |
client.from('posts').update({ title: 'Updated' }).eq('id', 1) |
update |
| Delete | .delete() |
client.from('posts').delete().eq('id', 1) |
delete |
| RPC | .rpc() |
client.rpc('function_name', { param: 'value' }) |
rpc |
Filters
Section titled “Filters”| Filter | Description | Example |
|---|---|---|
.eq() |
Equals | .eq('status', 'published') |
.neq() |
Not equals | .neq('status', 'draft') |
.gt() |
Greater than | .gt('price', 100) |
.lt() |
Less than | .lt('price', 50) |
.gte() |
Greater than or equal | .gte('quantity', 1) |
.lte() |
Less than or equal | .lte('quantity', 10) |
.like() |
Pattern match (case-sensitive) | .like('title', '%hello%') |
.ilike() |
Pattern match (case-insensitive) | .ilike('title', '%hello%') |
.is() |
Is null / not null | .is('deleted_at', null) |
.in() |
Value in array | .in('status', ['active', 'pending']) |
Modifiers
Section titled “Modifiers”| Modifier | Description | Example |
|---|---|---|
.order() |
Sort results | .order('created_at', { ascending: false }) |
.limit() |
Limit rows returned | .limit(10) |
.single() |
Return single row | .select('*').eq('id', 1).single() |
For the complete list of methods and detailed examples, see the Neon TypeScript SDK.
Next steps
Section titled “Next steps”- Set up Managed Better Auth: Managed authentication with JWTs that work natively with the Data API and Row Level Security
- Build a note-taking app: Hands-on tutorial with Data API queries
- Neon TypeScript SDK: All database methods: select, insert, update, delete, filters, and more
- Generate TypeScript types: Get autocomplete for table names and columns
- SQL to REST Converter: Convert SQL queries to API calls
- Row-Level Security with Neon: Secure your data at the database level